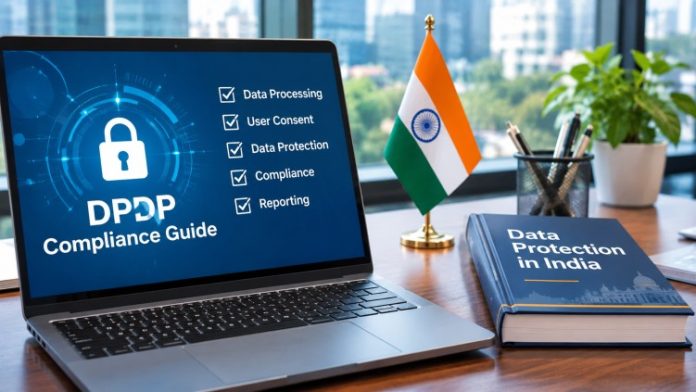
Singahi has released a comprehensive compliance guide aimed at assisting software, cloud, IT, and outsourcing companies in navigating the data protection requirements of India’s Digital Personal Data Protection (DPDP) Act, 2023. This guide, titled “Processing personal data for Indian clients: the DPDP questions you will be asked,” offers insights into 12 key questions that suppliers managing personal information on behalf of Indian businesses might face during contract renewals and compliance assessments. As the majority of the Act’s provisions are scheduled to take effect from May 13, 2027, it becomes crucial for organizations processing personal data to start preparing.
The DPDP Rules, 2025, were notified by the Ministry of Electronics and Information Technology on November 13, 2025, setting the stage for the legislation’s implementation. While certain provisions, like the establishment of the Data Protection Board, took effect immediately, other requirements, such as those for consent managers, will begin on November 13, 2026. Key obligations concerning security safeguards, breach reporting, data erasure, individual rights, and penalties will apply from May 13, 2027. Under section 8(1) of the Act, Data Fiduciaries are held accountable for processing activities conducted by their Data Processors, regardless of contractual terms.
Singahi’s guide delves into several critical areas, including contractual responsibilities, information security, breach notifications, individual rights, data erasure, sub-processors, and audit requirements. It references relevant sections of the Act and provisions of the Rules, while aligning its guidance with ISO/IEC 27701, an international standard for privacy information management. The guide also underscores the financial repercussions of non-compliance, noting penalties up to ₹250 crore for failures related to reasonable security safeguards, and up to ₹200 crore for not notifying personal data breaches. Rule 6(1)(f) mandates that contracts between Data Fiduciaries and Data Processors include provisions for reasonable security safeguards.
Incident reporting receives particular emphasis in the guide, as delays by service providers can impede a client’s ability to comply with statutory deadlines. Rule 7 obliges Data Fiduciaries to notify affected individuals and the Data Protection Board promptly, followed by a detailed report to the Board within 72 hours of becoming aware of a breach. Additionally, specified cyber incidents must be reported to CERT-In within six hours, in accordance with its Directions from April 28, 2022. Rahul Verma, a Cybersecurity Sales Specialist at Singahi, advised that suppliers prioritize breach notification clauses, followed by provisions concerning sub-processors and data deletion upon contract termination.
The guide also addresses practical evidence requirements, including data retention and audit readiness. One example from the DPDP Rules involves a company using a cloud provider to host customer records, requiring the provider to retain relevant data and logs for a year before erasure. Although the legislation does not demand ISO 27701 certification for Data Processors, Significant Data Fiduciaries must appoint independent data auditors and conduct a Data Protection Impact Assessment and audit every year. Singahi’s guide concludes by recommending seven documents that suppliers should prepare, starting with the processing agreement, and offers a connection to its ISO 27701 toolkit, which includes 43 plain-language guides and free Control Packs with practical templates.
About Singahi
Singahi helps growing companies prove security to customers, investors and regulators. One team for compliance, testing, and managed security. Singahi is headquartered in Lucknow, India, with representatives in Bengaluru, Noida and Chandigarh.
Rahul Verma
Singahi Technologies Private Limited
+91 95802 30300
[email protected]
Legal Disclaimer:
The information contained in this article has been provided by independent third-party contributors, clients, or content partners. We do not independently verify the accuracy, completeness, legality, ownership, licensing, or reliability of submitted content, including text, images, videos, trademarks, or other media materials. The submitting party is solely responsible for ensuring that all content, including images and media assets, complies with applicable copyright, trademark, licensing, and intellectual property laws. We disclaim liability for any unauthorized use of copyrighted or proprietary materials by third parties. If you believe that any content published on this platform infringes your intellectual property rights, kindly contact the author above for prompt review and resolution.